ACCESS CONTROL SECURITY · 25 OCTOBER 2026
OSDP secure access control: a commissioning worksheet
A network door controller can be well protected while the short cable between its reader and controller remains the weak link. This worksheet helps builders, facility teams and integrators verify OSDP wiring, addressing, supervision, Secure Channel operation, door events and video integration as one accepted system.
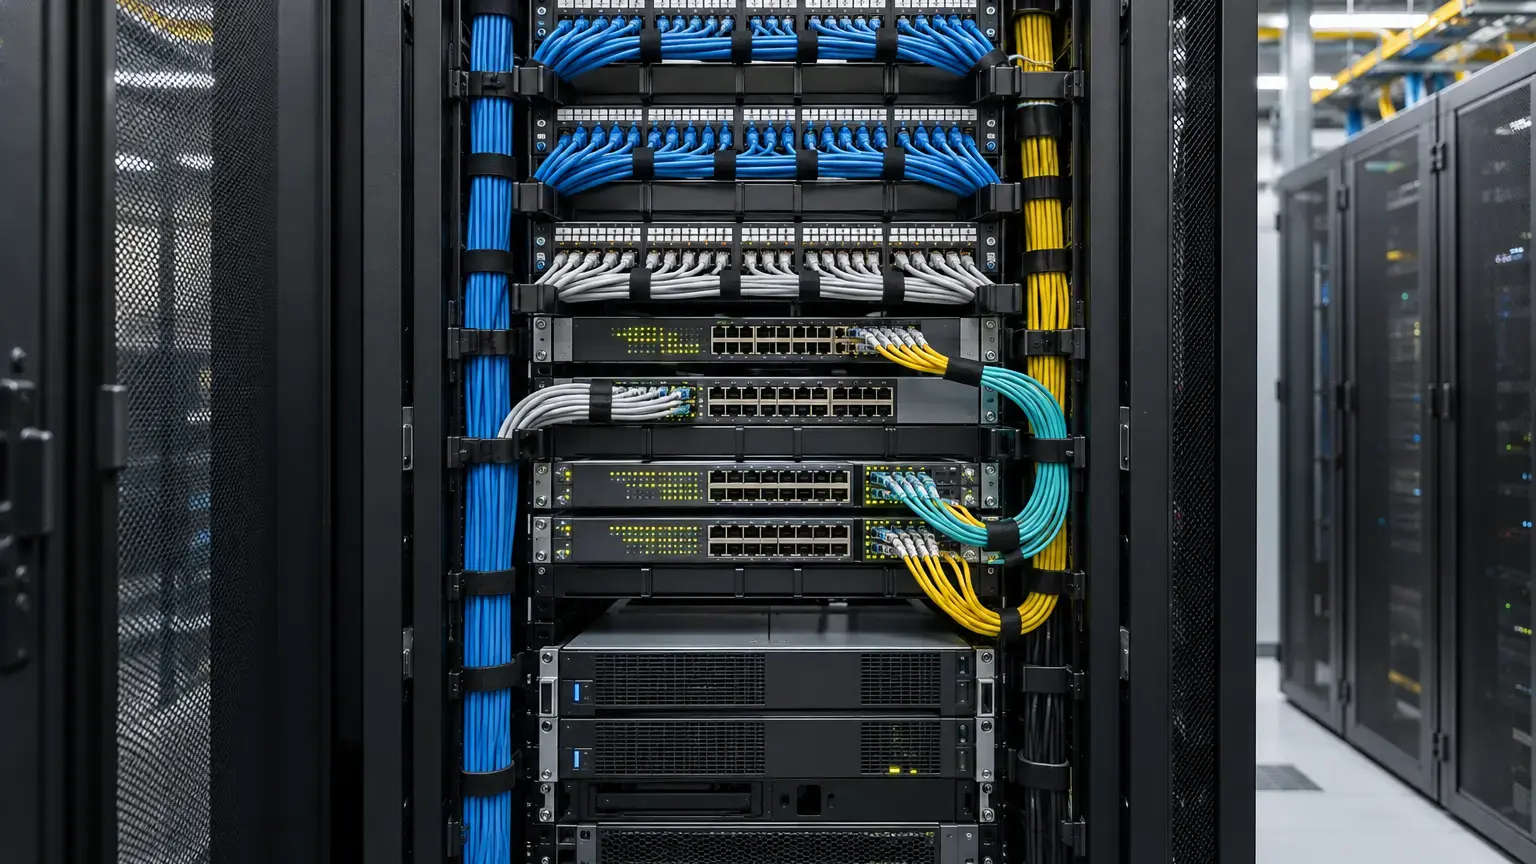
Visual reference photographs
Why OSDP changes the handover
Legacy Wiegand normally sends credential bits in one direction from reader to controller. OSDP is a bidirectional, supervised protocol intended for access-control peripheral communication. The Security Industry Association OSDP overview identifies Secure Channel support, wiring supervision and interoperability as central benefits. Its current implementation checklist also warns that unsecured mode should be limited to initialization before Secure Channel is established.
A reader that opens a door is therefore not enough. The record must prove which reader address was commissioned, which controller port or bus owns it, whether communication is supervised, whether Secure Channel is active with a non-default key, how offline and tamper states are reported, and whether the configuration survives a controlled restart.
Asset row: door ID · reader ID · controller and port · OSDP address · cable ID · power source · firmware · verified-product status · secure mode · key-change date · evidence filename.
Confirm product support before cabling
Do not assume that two products marked OSDP support every feature together. Record the exact controller, reader and firmware versions, then check manufacturer compatibility documentation and SIA OSDP Verified status where applicable. Verified status improves confidence in interoperability, but the installed combination still needs a field test.
Decide whether the design uses one reader per bus segment or multidrop operation. Confirm the supported device count, unique addressing, cable type, total distance, topology, termination and power limits from the selected manufacturers. RS-485 practice and OSDP product limits matter: a star-shaped field splice that appears convenient may create reflections and intermittent communication. Keep reader power voltage-drop calculations separate from data-bus length checks.
Calculate the reader power path
For each reader, record the manufacturer's maximum current at the intended voltage, not only an idle reading. Add any keypad, biometric or display load that belongs to the unit. Use the complete conductor loop length when estimating voltage drop.
Voltage-drop method: estimated drop = load current × total loop resistance. Estimated reader voltage = supply voltage - estimated drop. Confirm the result against the reader's permitted input range, then measure voltage at the reader in its highest agreed operating state.
Keep lock power out of the reader calculation unless the selected architecture explicitly shares a supply and the manufacturer permits it. Door strikes, magnetic locks and operators can introduce much larger loads and transients. Document controller supply, reader output limit, auxiliary supply, battery backup and the common reference or isolation arrangement required by the equipment.
Commission addressing before Secure Channel
Build an address plan before connecting multiple devices. Use a unique address for every reader on a bus and label the physical reader with its logical door and reader ID. Bring devices online in a controlled sequence so that duplicate addresses, reversed data conductors and unsupported settings are found early.
Unsecured installation mode is a commissioning state, not a final condition. After communication is stable, establish Secure Channel according to the controller and reader procedures. Replace installer or default keys with site-controlled keys. HID's guidance on legacy downgrade attacks recommends OSDP secure mode with non-default keys wherever practical and explains the risk of leaving default secure-channel keys in service.
Never place operational keys in the general as-built drawing or an unrestricted spreadsheet. The handover should identify the key owner, approved escrow or recovery method, date of initialization and controlled replacement procedure without exposing the key value.
Prove Secure Channel, supervision and downgrade resistance
Capture controller evidence that shows the reader online in secure mode. Then perform controlled tests agreed with the manufacturer: disconnect the data pair, remove reader power, open the enclosure tamper where supported, reconnect the device and restart the controller. Record the alarm or event, time to detection, operator message, restoration behavior and whether secure operation is re-established.
Where the platform allows policy enforcement, verify that a commissioned reader cannot silently return to unsecured mode. SIA's February 2026 OSDP implementation checklist calls for Secure Channel and recommends disabling legacy protocols when they are not required. Record any exception, reason, compensating control, owner and correction date.
Security-state test row: test ID · initial secure status · action · expected event · observed event · detection time · secure status after recovery · evidence · result · exception owner.
Do not confuse a converter with end-to-end secure communication
A converter can help retain a legacy reader when a controller provides OSDP ports. For example, the Axis TA1101-B documentation describes one converter for each Wiegand reader. This can secure and supervise the OSDP segment between converter and controller, but it does not turn the reader-to-converter Wiegand wires into OSDP. Record the converter location and the boundary between legacy and secure communication so the risk is visible.
Where a converter is used, place it as close to the legacy reader as the supported installation allows, protect its enclosure and tamper state, and test removal or substitution. The exact placement and wiring must follow the selected product documentation.
Test the complete door and video association
For every door, test valid access, invalid credential, door held open, door forced open, request-to-exit, lock release, door-position feedback, reader tamper and controller offline behavior. Confirm the event name, door identity, timestamp, operator action and audit trail. If fire-alarm release, lift control, turnstiles or visitor systems are integrated, use an approved cause-and-effect matrix and involve the responsible specialist.
Where access events call up video, verify the mapping in both directions. Present a credential and confirm that the correct camera, time window and door event appear. Trigger forced-door and held-door events and verify recording, bookmark or alarm behavior. The access system and CCTV system must use a coordinated time source. Treat biometric templates and access logs as controlled personal data under the project's applicable policy and legal advice.
OSDP commissioning checklist
- Every door, reader, controller, port, cable and power source has a unique identifier.
- Exact models, firmware and supported OSDP features are recorded.
- Verified status and manufacturer compatibility references are retained where available.
- Bus topology, length, cable type, termination and device count follow equipment limits.
- Each multidrop device has a unique documented address.
- Reader voltage drop is calculated and measured at the highest agreed operating load.
- Installer or default Secure Channel keys are replaced under a controlled process.
- Final controller evidence shows the reader online in secure mode.
- Unsecured fallback and unused legacy interfaces are disabled where supported and required.
- Communication loss, power loss, tamper and recovery events are witnessed.
- Secure operation returns after controller and reader restart.
- Valid, invalid, forced, held-open and request-to-exit cases are tested.
- Lock behavior, door-position feedback and backup-power outcome are recorded.
- CCTV event association and timestamps are tested where integrated.
- Configuration backups, key ownership, recovery procedure and change responsibility are handed over securely.
- Exceptions have an owner, due date, corrective action and retest evidence.
Minimum handover pack
Provide the door and reader schedule, controller inventory, bus and cable drawing, address plan, power and voltage-drop worksheet, firmware record, secure-state evidence, controlled key-management statement, event matrix, backup-power results, video-integration test, configuration backup, exception register and signed acceptance sheet. Link these records to the intercom and gate-access handover worksheet and CCTV time synchronization worksheet where systems share events.
Planning secure access control for a commercial or residential project?
Share the door schedule, reader and controller selections, cabling routes, power design, integration matrix and acceptance requirement. We can coordinate the ELV network, access-control infrastructure, CCTV integration and field handover records around the approved scope.
Discuss access control ↗